Mobile App Security

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg
Showing posts with label Security; Identity Management. Show all posts

Tuesday, 26 November 2013

NSA 'infected' 50,000 networks with malware

Posted on 18:53 by Unknown
25 November 2013 Last updated at 07:05 ET BBC

Share this page

  • Email
  • Print
1.6K
  • Share
  • Facebook
  • Twitter
Belgacom head officeThe NSA and GCHQ are alleged to have installed malware on the networks of targets including the Belgian telecoms firm Belgacom
Continue reading the main story

Related Stories

  • The new meaning of spyware
  • Web inventor in surveillance warning
  • Yahoo to encrypt all users' data
The US National Security Agency (NSA) infected 50,000 networks with malware, Dutch newspaper NRC has reported.
The Tailored Access Operations department used it to steal sensitive information, according to a censored slide leaked by former NSA contractor Edward Snowden.
NRC said 20,000 networks had been hit in 2008, with the program recently expanded to include others in Rome, Berlin, Pristina, Kinshasa, Rangoon.
The NSA declined to comment.
The malware could be put in a "sleeper" mode and activated with a click of a button, the paper said.
"Clearly, conventional criminal gangs aren't the only people interested in breaking into computer networks anymore," wrote computer security expert Graham Cluley in a blogpost.
"All organisations need to ask themselves the question of whether they could be at risk."
The reports come as Twitter introduces technology it says will help protect people's messages from unwanted scrutiny.
It has employed a system known as "forward secrecy" that makes it harder for eavesdroppers to access the keys used to encrypt data passing between Twitter's servers and users' phones, tablets and PCs.
Read More
Posted in Industry News, James Jones, Security, Security; Identity Management | No comments

Friday, 22 November 2013

Tim Berners-Lee says 'surveillance threatens web'

Posted on 08:58 by Unknown
21 November 2013 Last updated at 19:24 ET  BBC

 
Sir Tim Berners-Lee said important issues had been raised by recent leaks


Web creator Sir Tim Berners-Lee has warned that the democratic nature of the net is threatened by a "growing tide of surveillance and censorship".

The warning came as he launched his World Wide Web Foundation's annual web index report, tracking global censorship.

It suggests that 94% of the countries in the index do not adequately monitor government internet interception.

Thirty per cent of countries block or filter political content, it indicates.

The report concludes that the current legal framework on government snooping needs urgent review.

"One of the most encouraging findings of this year's web index is how the web and social media are increasingly spurring people to organise, take action and try to expose wrongdoing in every region of the world," said Sir Tim.

"But some governments are threatened by this, and a growing tide of surveillance and censorship now threatens the future of democracy.

Bold steps are needed now to protect our fundamental rights to privacy and freedom of opinion and association online," he added.
'Appalling and foolish'

Sir Tim has been an outspoken critic of government surveillance following the revelations from whistle-blower Edward Snowden.

He described attempts by the spy agencies to crack encryption as "appalling and foolish".

He has previously said that the checks and balances to oversee GCHQ and its US counterpart, the National Security Agency (NSA), have failed.

It is a view shared by digital forensic expert Professor Peter Sommer.

"GCHQ is a spying agency. It needs to produce good results. But how far anyone understands the techniques they are using is more unclear."

"The things they are doing need a ministerial warrant but the ministers have a lot of other things to do. Did they have sufficient understanding of the technology? Who is doing the risk analysis?"

A Cabinet Office spokesperson told the BBC: "The success of our intelligence agencies relies on secrecy. But secrecy does not mean lack of accountability. The United Kingdom's intelligence agencies operate under the tightest of controls and oversights.

"Our agencies only act in line with their strict legal mission, above all keeping people safe from harm.

"There is a triple lock to ensure every action is lawful, necessary and proportionate - interception underpinned by Ministerial warrants, world class internal controls and three safety nets of outside scrutiny by the Interception Commissioner, the Intelligence and Security Committee of Parliament and the Investigatory Powers Tribunal." Measure of influence

The report compiled by Sir Tim's World Wide Web Foundation ranks countries in terms of the social and political impact of the web.

Sweden tops the annual web index, ahead of Norway, and followed by the UK, US and New Zealand.

It found that in 80% of the countries studied, the web and social media played a role in mobilising the public on a range of issues.

It also found that rich countries did not necessarily rank higher in the index. The Philippines, with a per-capita income of $4,410 per year, is more than 10 places ahead of Qatar, the world's richest country.

Meanwhile Saudi Arabia is outperformed by 10 sub-Saharan African countries, and Switzerland, the third wealthiest nation, is only one place ahead of Estonia.

But in poorer countries the digital divide is growing ever more marked, according to the report.

"Ten years after world leaders committed to harnessing technology to build an inclusive information society, parents in 48% of countries can't use the web to compare school performances and budgets, women in over 60% of countries can't use the web to help them make informed choices about their bodies, and over half the population in developing countries can't use the web at all," said Anne Jellema, the foundation's chief executive.
Read More
Posted in ethics, ICT Education, James Jones, Security, Security; Identity Management, Web | No comments

Tuesday, 19 November 2013

HP: 90% of Apple iOS mobile apps show security vulnerabilities

Posted on 13:59 by Unknown
Testing of more than 2,000 mobile apps developed by corporations reveals serious flaws

By Ellen Messmer, Network World
November 18, 2013 12:12 PM ET

Network World - HP today said security testing it conducted on more than 2,000 Apple iOS mobile apps developed for commercial use by some 600 large companies in 50 countries showed that nine out of 10 had serious vulnerabilities.

Mike Armistead, HP vice president and general manager, said testing was done on apps from 22 iTunes App Store categories that are used for business-to-consumer or business-to-business purposes, such as banking or retailing. HP said 97% of these apps inappropriately accessed private information sources within a device, and 86% proved to be vulnerable to attacks such as SQL injection.


The Apple guidelines for developing iOS apps help developers but this doesn’t go far enough in terms of security, says Armistead. Mobile apps are being used to extend the corporate website to mobile devices, but companies in the process “are opening up their attack surfaces,” he says.

In its summary of the testing, HP said 86% of the apps tested lacked the means to protect themselves from common exploits, such as misuse of encrypted data, cross-site scripting and insecure transmission of data.

Businesses offer best practices for escaping CryptoLocker hell

The same number did not have optimized security built in the early part of the development process, according to HP. Three quarters “did not use proper encryption techniques when storing data on mobile devices, which leaves unencrypted data accessible to an attacker.” A large number of the apps didn’t implement SSL/HTTPS correctly.
To discover weaknesses in apps, developers need to involve practices such as app scanning for security, penetration testing and a secure coding development life-cycle approach, HP advises.

The need to develop mobile apps quickly for business purposes is one of the main contributing factors leading to weaknesses in these apps made available for public download, according to HP. And the weakness on the mobile side is impacting the server side as well.

“It is our earnest belief that the pace and cost of development in the mobile space has hampered security efforts,” HP says in its report, adding that “mobile application security is still in its infancy.”

Ellen Messmer is senior editor at Network World, an IDG publication and website, where she covers news and technology trends related to information security. Twitter: MessmerE.
Read More
Posted in Computer Science, ICT Applications, ICT Research, Industry News, James Jones, Mobility, Security, Security; Identity Management, Web | No comments

Monday, 18 November 2013

Guardian: Cyber-attacks eclipsing terrorism as gravest domestic threat – FBI

Posted on 12:48 by Unknown
Counter-terrorism chiefs urge Congress to resist altering controversial surveillance programs except 'at the margins'

Spencer Ackerman in New York

theguardian.com, Thursday 14 November 2013 13.06 EST


FBI director James Comey listens to Homeland Security secretary Rand Beers testify before a Senate panel. Photograph: Michael Reynolds/EPA

The threat of a major terrorist attack inside the United States is lower today than before 2001, three of the country’s most senior counter-terrorism officials testified on Thursday.

But the heads of the FBI, Department of Homeland Security and National Counterterrorism Center urged Congress only to change controversial surveillance programs at the “margins".

A devastating, 9/11-style attack is “more likely now to be overseas than it is in the homeland”, Rand Beers, the acting secretary of the Department of Homeland Security, told a Senate panel, “but that is not to say we should drop our guard in any way”.

Testifying for the first time since becoming FBI director in September, James Comey told the Senate homeland security and government affairs committee that cyber-attacks were likely to eclipse terrorism as a domestic danger over the next decade.

“That’s where the bad guys will go,” Comey said. “There are no safe neighborhoods. All of us are neighbors [online].”

Comey said the threat to online networks in the United States, to include business and government data, came from disparate actors with different motivations, from spies to “hacktivists”, which he likened to an “evil layer cake”.

Cyber-security concerns eclipsed those about terrorism in a hearing dedicated to updating the Senate on domestic threats. Beers and Comey urged Congress to pass new cyber-security legislation expanding government access to private-sector data, ostensibly to redress vulnerabilities in business and other non-governmental networks.

Senator Tom Coburn, the top Republican on the panel, sounded skeptical, arguing that private firms ought to have the opportunity to voluntarily comply before being compelled to turn over that data. But Coburn agreed with Beers that any such legislation ought to provide legal protections for companies compelled to disclose proprietary or customer data.

Beers said legislation ought to be “carefully crafted” to avoid “a total blanket liability protection”, which he said would potentially violate civil liberties.

Congress created similar protections for telecommunications and internet providers in 2008 when it expanded the government’s powers to spy on Americans’ foreign communications with non-individualized warrants.

Comey, Beers and NCTC director Matthew Olsen testified that al-Qaida’s ability to attack the US was diminished, but not eliminated. “The risk of a spectacular attack in the homeland is much smaller than it was before 2001,” Comey said.

But all three individuals said the threat of copycat attacks from self-radicalized individuals – so-called “lone wolves” – remained, and they said the agencies had difficulties in preventing them.

Self-radicalized terrorists do not necessarily “hit the trip wires”, Olsen said. Comey urged Americans to report what they considered suspicious activity: “Listen to that feeling in back of your neck.”

Even though the threat of a major domestic terrorist attack has receded, all three government officials warned Congress against rolling back the sweeping bulk surveillance authorities granted to intelligence and law enforcement agencies to prevent one.

Comey, who in 2004 resisted a warrantless surveillance effort that collected Americans’ email data, told the Senate panel he could accept changes around the “margins” of surveillance powers, but “don’t make changes at the expense of core capabilities”.

Beers, who will soon leave the Department of Homeland Security after five years, echoed intelligence officials who have resisted surveillance reforms beyond increased transparency to Congress.

“Make sure you are comfortable with the oversight,” Beers said, “but don't throw the baby out with the bathwater.”
Read More
Posted in Industry News, James Jones, Networking, Security, Security; Identity Management, Web | No comments

Thursday, 14 November 2013

IASE Unclassified Cyber Awareness Challenge

Posted on 16:01 by Unknown
Following are links to good training and assessment simulations for ICT User security developed and used by the U.S. military and Federal government.  Check them out for your digital literacy courses and programs.  Everyone, no matter what their industry or job is, should have this level of knowledge.

From webpage at IASE

CyberAwareness Challenge

Department of Defense Employees


Launch New CyberAwareness Challenge Department of Defense Version
Continue Current CyberAwareness Challenge Department of Defense Version

Federal Employees


Launch New CyberAwareness Challenge Federal Version
Continue Current CyberAwareness Challenge Federal Version


Product Functionality Caution: To meet technical functionality requirements, this awareness product was developed to function with Windows operating systems (Windows 7, VISTA, and XP, when configured correctly) using either the Internet Explorer (IE) or Firefox browsers. Users employing another OS or browser may experience difficulties and may not be able to complete the training or print the certificate of completion. If you have questions regarding this requirement, please contact the IASE Helpdesk.

Troubleshooting Guide
Testing support for...
JavaScript: Meets the criteria to run this courseware
Browser Version: Test indicates that this is not configured appropriately to run this courseware. You may still be able to run the courseware, however if you experience problems, please see below for instructions on how to troubleshoot issues
Cookies Enabled: Meets the criteria to run this courseware
Session Cookies Enabled: Meets the criteria to run this courseware
Flash 10+: Meets the criteria to run this courseware
Popup blocker: Meets the criteria to run this courseware
It appears that your browser configuration may not meet all of the requirements to run this courseware. See the Troubleshooting Guide for assistance.
Read More
Posted in Digital Literacy, ICT Education, James Jones, Security, Security; Identity Management | No comments

Wednesday, 13 November 2013

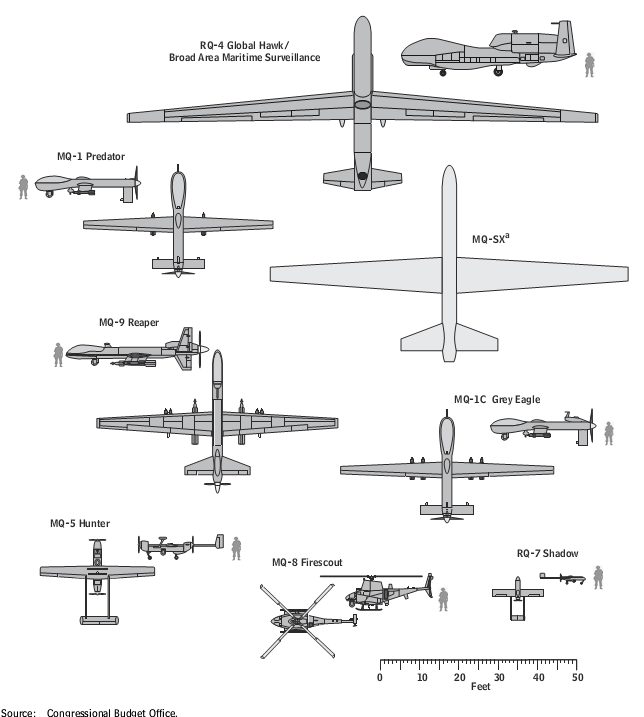
Here Come the WiFi Drones

Posted on 10:05 by Unknown

Dan Jones, Mobile Editor, 11/11/2013, LightReading
By the fall of 2015, nonmilitary unmanned aircraft (drones) are set to be flying in US airspace, and at least some will be equipped with WiFi and other communications equipment. This scenario could stir up new issues around security and privacy on terra firma.

Last week, the Federal Aviation Administration sent its plan for the "safe acceleration of the integration of civil UAS [unmanned aircraft systems] into the National Airspace System" (NAS) to several government transportation committees. The plan calls for commercial drones to be flying "not later than September 30, 2015" and earlier if possible.

The agency says drones could be used for anything from crime scene investigations to border patrol and search and rescue missions. The New York Police Department has already expressed interest in using unmanned aircraft as a surveillance tool. The FAA is also expecting drones to be used in agricultural applications.

At least 81 public organizations in the US have applied for special certification from the FAA to fly drones in domestic airspace, according to a list obtained by the Electronic Frontier Foundation . These include universities and local police and fire departments.

The FAA is defining -- and refining -- a plan for the safe integration of drones into US airspace. Operator training and collision sensors are seen as crucial, given the many types and sizes of drones expected to arrive in US airspace.

Such measures are important for flight safety. CNN reported this spring that a mysterious drone came within 200 feet of a commercial jetliner above John F. Kennedy Airport in New York. Drones could damage or down commercial aircraft by crashing into them or being sucked into a jet engine of the plane, depending on the unmanned craft's size.

The privacy issues around the use of drones are cloudier. The FAA states in the report:

Although there is no Federal law that specifically addresses privacy concerns with respect to civil UAS operations, many states have laws that protect individuals from invasions of privacy which could be applied to intrusions committed by using a UAS.
Integrating public and civil UAS into the NAS carries certain national security implications, including cyber and communications security, domestic framework for US government operations, national airspace and defense, airman vetting/general aviation, and privacy concerns. In coordination with the National Security Staff at the White House, the FAA is working in conjunction with relevant agency partners on an Interagency Policy Committee to address these issues.

This could lead to some interesting concerns about WiFi snooping and other communications surveillance using drones, particularly in the current climate. The burgeoning hobbyist industry for small drones has already shown how easy it is to install WiFi as a control mechanism on remote controlled aircraft. Hobbyist drones can already be flown in the US at 400 feet and below and within sight of the operator. Companies such as Parrot SA make WiFi-equipped quadricopters for drone fanciers.

Adam Conway, vice president of product management at Aerohive Networks Inc. , told us his company has already been experimenting with a WiFi access point in a drone. It flew a drone a few hundred feet above Sunnyvale, Calif., with a hotspot with a 4G module on board and got connected. Such temporary WiFi could obviously provide connectivity in disaster recovery situations and remote areas. However, there are many ways to use WiFi for snooping on other 802.11 users.

Brendan O'Connor, a law student at the University of Wisconsin at Madison and a researcher at the consulting firm Malice Afterthought, recently demonstrated the capabilities of CreepyDOL, a tiny and cheap WiFi sensor that can gather information about iPhone users as they walk around their neighborhood. Google (Nasdaq: GOOG) is battling a class action after it collected unencrypted WiFi data when its Google Maps cars took more than just snaps of areas around the world.

With ever-quieter drones being developed, it's possible to see how unmanned aircraft could be used as a surveillance and data collection tool in US airspace in the coming years. And it's hard to imagine that the topic of spying and snooping won't still be high on the public agenda come September 2015. (See: Another Day, Another Domestic Spying Revelation.)

— Dan Jones, Mobile Editor, Light Reading
Read More
Posted in Industry News, James Jones, Mobility, Networking, networking security, Security, Security; Identity Management, Web, Wireless | No comments

Monday, 28 October 2013

Protesters Call for an End to NSA Mass Surveillance

Posted on 12:13 by Unknown

About 5,000 people attend a rally in Washington to protest NSA programs

 By Grant Gross
Sat, October 26, 2013 CIO

IDG News Service (Washington, D.C., Bureau) — A crowd of about 5,000 people, chanting "stop spying, stop lying" and "hey, ho, mass surveillance has got to go," marched through Washington, D.C., Saturday to protest the U.S. National Security Agency's mass surveillance programs unveiled in press reports this year.

Protesters, from a seemingly wide range of political beliefs, called on the U.S. Congress and President Barack Obama to end mass data collection and surveillance by the NSA.

"The government has granted itself power that it does not have," said former New Mexico Governor Gary Johnson, the 2012 Libertarian Party candidate for U.S. president. "We have to stand against this."

Hundreds in the crowd held signs or wore stickers thanking Edward Snowden, the former NSA contractor whose leaks to news organizations exposed mass surveillance and data collection programs at the spy agency. Others held signs with the text of the Fourth Amendment to the U.S. Constitution, which protests residents against unreasonable searches and seizures.

Another popular sticker, from antiwar group Code Pink, featured lipstick marks and the message, "Make out, not war."

During the rally, members of the groups Fight for the Future and Restore the Fourth delivered a petition, with more than 575,000 signatures, calling on Congress to investigate NSA surveillance programs, to Representative Justin Amash, a Michigan Republican an outspoken critic of the NSA surveillance programs.

Many politicians want people to believe that a small group of people can't make a difference in the U.S. government, said Craig Aaron, president and CEO of digital rights group Free Press. "It's not such a small group," he told the crowd. "There are millions of people siding with us."

The rally, organized by the StopWatching.us coalition, was held on the 12th anniversary of the date former U.S. President George W. Bush signed the controversial Patriot Act into law. The NSA has used portions of the Patriot Act as the foundation for its mass surveillance programs. Protests were also scheduled in a handful of other cities in the U.S. and Germany.

The NSA and members of the Obama administration have defended the data collection and surveillance programs as necessary to protect the U.S. against terrorism. While the NSA collects phone records in bulk, the agency only obtains content for phone calls when it suspects criminal activity, Obama administration officials have said.

Rally attendees said it was important for them to be at the event, although some were unsure if it would make a difference.

Showing up at the rally was a way of "doing something" instead of just complaining about the NSA, said Lauren Schreiber, community outreach and event coordinator at the Council on American Islamic Relations in Washington, D.C.

The Muslim community in the U.S. has long been the target of surveillance, she noted. "I feel like if the government doesn't respect the very basic right of privacy, then all of our other rights are going to be trampled," she said.

Paul Charnetzki IV traveled to Washington from Chicago to attend the rally. He's opposed to the increased surveillance in the U.S. since the Sept. 11, 2001, terrorist attacks on the U.S., he said.

Asked if the rally would make a difference, Charnetzki said, "Who knows?" He talked to a staffer at his congressman's office before the rally, and the staffer questioned if he was an extremist, he said.

"It got a little tense in there," he added.

The U.S. government needs to return to the protections of the Fourth Amendment, added John Lambert, from central Virginia. The U.S. government also needs to stop its surveillance on foreign leaders, he said, noting news reports this week.

"Spying on Americans without warrants is illegal," he said. "Spying on allies is just stupid."

Grant Gross covers technology and telecom policy in the U.S. government for The IDG News Service. Follow Grant on Twitter at GrantGross. Grant's email address is grant_gross@idg.com.
Read More
Posted in Digital Literacy, ICT Regulation, Industry News, James Jones, law, Security, Security; Identity Management | No comments

Friday, 25 October 2013

MEPs vote to suspend US data sharing

Posted on 19:31 by Unknown
24 October 2013 Last updated at 08:52 ET BBC

Edward Snowden, NSA whistleblower
Leaked documents allege bank data unrelated to terrorism was shared with US

The European Parliament has voted to suspend the sharing of financial data with the US, following allegations that citizens' data was spied on.

The allegation forms part of leaked documents from whistleblower Edward Snowden.

The vote is non-binding but illustrates MEPs' growing unease over how much data was shared with the US.

It comes a day after it was alleged that German Chancellor Angela Merkel's mobile phone calls were monitored.

The European Parliament voted to suspend its Terrorist Finance Tracking Program (TFTP) agreement with the US, in response to the alleged tapping of EU citizens' bank data held by the Belgian company SWIFT.

The agreement granted the US authorities access to bank data for terror-related investigations but leaked documents made public by whistleblower Edward Snowden allege that the global bank transfer network was the target of wider US surveillance.

MEPs also want to launch a full inquiry into the alleged spying.
Merkel phone
The row over exactly how much snooping was done on European citizens appears to be escalating.

Germany has summoned the US ambassador in Berlin over the claims that the US monitored Mrs Merkel's mobile phone calls.

Other leaders are also likely to want further clarification from Washington over the activities of its National Security Agency (NSA) in Europe.

Meanwhile student group, europe v facebook, is launching a fresh attack on how deeply the social network was involved in the US spying programme.

It has won the right for a review of why the Irish data protection commissioner is not investigating the amount of European data shared with the US.

Commissioner Billy Hawkes has previously claimed that there "is nothing to investigate" over Facebook's role in the PRISM programme.

Max Schrem, who heads the group, remains unconvinced.

"When it comes to the fundamental rights of millions of users and the biggest surveillance scandal in years, he will have to take responsibility and do something about it," he said.
Read More
Posted in ICT Regulation, James Jones, law, Security, Security; Identity Management | No comments

Sunday, 20 October 2013

Ted Talk: James Lyne: Everyday cybercrime -- and what you can do about it

Posted on 11:58 by Unknown
Ted Talk

How do you pick up a malicious online virus, the kind of malware that snoops on your data and taps your bank account? Often, it's through simple things you do each day without thinking twice. James Lyne reminds us that it's not only the NSA that's watching us, but ever-more-sophisticated cybercriminals, who exploit both weak code and trusting human nature.
   
Whether he’s taking on insecure hotspots, inept passwords, or lax OS designers, James Lyne exposes technology’s vulnerabilities while elevating the security awareness of everyday users. Full bio »


Read More
Posted in Digital Literacy, James Jones, Security, Security; Identity Management | No comments

Tuesday, 15 October 2013

California governor vetoes state email privacy bill

Posted on 14:23 by Unknown
By Kate Tummarello - 10/14/13 03:37 PM ET The Hill

California Gov. Jerry Brown (D) vetoed a state online privacy bill that would have protected residents’ electronic communications accounts from warrantless access by law enforcement agencies.

The bill would require law enforcement agencies to obtain a warrant before accessing electronic communications. They would have to notify a user within three days of accessing that user’s electronic communications.

Under current federal law, the Electronic Communications Privacy Act (ECPA), law enforcement agencies do not need warrants to require electronic communication companies to turn over their users’ communications if they have been electronically stored for more than 180 days.

If law enforcement agencies do obtain a warrant, they do not have to notify the user. If they have subpoenas or court orders — which have a lower burden of proof than warrants — they are required to inform the user.

Led by Senate Judiciary Committee Chairman Patrick Leahy (D-Vt.), Congress is considering ECPA reform but has yet to pass legislation updating the 27-year-old law.

These expanded notice requirements in the California bill “go beyond those required by federal law and could impede ongoing criminal investigations,” Brown wrote in his veto statement on Saturday.

“I do not think that is wise.”

Brown’s concerns are “overblown,” according to Hanni Fakhoury, staff attorney at the Electronic Frontier Foundation (EFF), which supported the bill.

The EFF wrote to Brown last month, encouraging him to sign the bill into law. The bill is “a sensible [one] that updates the state’s electronic privacy laws to the realities of the 21st century,” the group wrote.

Fakhoury said privacy advocates have been optimistic that states will pass privacy-enhancing legislation where the federal government has tried to and failed, especially now that Congress is mired in the shutdown and debt-ceiling debates.

“Our hope has been to get states to jump in and fill the voids,” he said.
Read More
Posted in Digital Literacy, ethics, ICT Education, James Jones, law, Security, Security; Identity Management | No comments

Wednesday, 25 September 2013

New California law will let minors digitally erase their online past

Posted on 09:39 by Unknown
By Bryan Bishop on September 23, 2013 08:41 pm The Verge


Earlier this year Google's Eric Schmidt suggested that the internet should have a "delete" button for individuals that wanted to remove troubling information from the web, and thanks to a new law minors in California will get that chance. The SFGate reports that California governor Jerry Brown signed a new law today that will require internet companies to pull down online activity from their services should a minor make the request. While the law is a step forward it has more than a few loopholes. Companies won't need to remove any data from their servers — they'll just need to take it offline — and it only covers photos, data, or other online activity that is generated by the requesting individuals themselves. Minors won't be able to force companies to pull information posted, or reposted, by others. It's scheduled to go into effect in 2015.

While most mainstream services already allow users to delete their accounts, the new law is the latest development in what's been a particularly proactive effort by California legislators to deal with online issues. The state already has provisions in place that ensure victims of domestic violence can have information pulled from the web, and last year it passed a law that prevents employers and universities from demanding Facebook login credentials from individuals.
Read More
Posted in Digital Literacy, ICT Regulation, Industry News, James Jones, Security, Security; Identity Management | No comments

Wednesday, 11 September 2013

Internet S.O.S.

Posted on 15:23 by Unknown
The Huffington Post, Timothy Karr, Campaign Director, Free Press and SavetheInternet.com

Posted: 09/10/2013 7:38 am 

Is the Internet on life support?

Last week we learned that U.S. and British intelligence agencies have broken the back of digital encryption -- the coded technology hundreds of millions of Internet users rely on to keep their communications private.

Over the weekend, Der Spiegel reported that the NSA and its British counterpart are also hacking into smartphones to monitor our daily lives in ways that wouldn't have been possible before the age of the iPhone.

This news, just the latest revelations from the files of Edward Snowden, only heighten our sense that we can no longer assume anything we say or do online is secure.


But that's not all. In a case heard before a U.S. federal appeals court on Monday, telecommunications colossus Verizon argued that the First Amendment gives it the right to block and censor Internet users. (That's right. Verizon is claiming that, as a corporation, it has the free speech right to silence the online expression of everybody else.)

Government and corporate forces often work together to chip away the two pillars of the open Internet: our ability to control our personal data and our right to connect and communicate without censorship or interference.

The Surveillance Industrial Complex

A series of reports coordinated among the Guardian, the New York Times and ProPublica revealed that the NSA and its British counterpart have secretly unlocked encryption technologies used by popular online services, including Google, Facebook and Microsoft.

Using National Security Letters and other secret court orders, intelligence agencies can wedge their way onto the large telecommunications networks that move most of the world's Internet traffic. Getting access to the data is only half the challenge. To read and sort these communications, the NSA works with a lesser-known assortment of security vendors that filter through mountains of data, target references and patterns of interest and crack codes designed to safeguard user identity and content.

Many of the companies that ply this trade are only now being exposed through "Spyfiles," collaboration among WikiLeaks, Corporate Watch and Privacy International designed to shed light on the multibillion-dollar industry. According to the latest documents provided by Edward Snowden, U.S. intelligence agencies alone spend $250 million each year to use these companies' commercial security products for mass surveillance.

It's part of a sprawling complex of companies, lobbyists and government officials seeking to rewire the Internet in ways that wrest control over content away from Internet users.

While motivations may differ, the result is the same: a communications network that works against the Interests of many for the benefit of the few.

Tearing the Fabric

The Internet wasn't meant to be like this. Bruce Schneier, an encryption fellow at Harvard's Berkman Center for Internet and Society, says that the NSA and the companies it works with are "undermining the very fabric of the Internet."

Telecommunications companies are doing their part by giving spy agencies access to our data. They're also bankrolling a multimillion-dollar lobbying effort to destroy Net Neutrality -- the one rule that prohibits Internet service providers from blocking or degrading our ability to connect to one another, share information and use the online services of our choosing.

If Verizon wins its case in Washington, ISPs will be able to prioritize certain online content while degrading user access to sites and services that the big companies don't like.

It's a business that puts at risk the most integral function of the World Wide Web. Sir Tim Berners-Lee, the Web's pioneer, saw the network as a "blank canvas" -- upon which anyone could contribute, communicate and innovate without permission.

Berners-Lee's invention relied on an open protocol that gave everyday users power over the network. This networking principle has far-reaching political implications, favoring systems that are more decentralized and democratic.

Without safeguards that protect users from surveillance and censorship, the Internet's DNA will change in ways that no longer foster openness, free expression and innovation.

Media Policy

If we've learned anything during the Summer of Snowden, it's that corporations and governments alone can't be trusted to be good stewards of the Internet.

We need media policies that protect our privacy and promote access to open networks.

The fight for these policies is being led by a diverse and bipartisan alliance of civil liberties and communications-rights organizations, including the ACLU, EFF, Free Press and Public Knowledge.

We're not alone. Millions joined the call for Net Neutrality in 2010; millions more stood up to defend the Internet against the PIPA and SOPA Web-censorship bills in 2012. The battle to protect users' privacy has engaged new audiences as we've learned more about the extent of the NSA's mass surveillance.

In each of these arenas, we're working to stop bad laws, amend others and implement new policies that put Internet users first.

A grassroots movement is fueling this fight. If you haven't joined us yet, now's the time to step up and save the Internet.

Follow Timothy Karr on Twitter: www.twitter.com/TimKarr
Read More
Posted in Industry News, James Jones, networking security, Security, Security; Identity Management, Web | No comments

Thursday, 5 September 2013

California Career Briefs: Start a Conversation

Posted on 10:13 by Unknown
                  
 
“Conversation costs nothing, but can bring you the world. ”
- Catherine Blyth, The Art of Conversation

Start a Conversation

Did you know?

In a flat, global economy the ability to connect and engage in critical conversations isn’t optional- it’s a survival skill. While e-mail, texting and social media have changed the way today’s students are interacting, these technologies encourage faceless and fragmented communication. We need to help our students branch out from the comfortable confines of their computer screens and cell phones and develop the face-to-face conversational confidence and experience they need in the professional world. After all, conversations build relationships; relationships build networks; and networks are a job seeker’s most valuable tool. This activity gives students an opportunity to make conversation connections to grow their personal and professional networks.

Try this…

  • Ask them…
    Why are conversational skills important in finding a job?
    How many face-to-face conversations do you have each day?
    How would you rate your conversational skills?
  • View video.
  • Demonstrate making a conversation connection with a student in class.
  • Distribute the Student Activity, review the directions and complete.
  • Find out how many people made a personal connection with their partners.

Add an Experience!

Identify several Professional Association networking opportunities in your community. Post these events and award credit for attending the event and making professional or personal connections with 2-3 attendees. Suggest students visit the CACareerCafe and learn to Network Like a Pro.
Read More
Posted in Diversity, ICT Education, James Jones, Security; Identity Management, Workforce Development | No comments

Thursday, 15 August 2013

National Cyber League (NCL) Fall 2013 Schedule Announcement

Posted on 11:43 by Unknown

The National Cyber League – Where Cybersecurity is a Passion

 
The National Cyber League (NCL) is pleased to announce its 2013 Fall Season Schedule!

General information, the event schedule and rules are available at: www.nationalcyberleague.org/fall13.shtml

The NCL mission is to offer engaging, entertaining, measurable, and scalable methods of learning to enlist a new generation of cybersecurity professionals.  Toward this end, the 2013 NCL Fall Season is designed to provide hands-on experiences and challenges that will enable players to practice and improve their cybersecurity skills - while having fun.

2013 Fall Season Highlights: 

·       Preparatory lab exercises and games to help prepare students for CompTIA Security+ and EC-Council Certified Ethical Hacker (CEH) certification exams

·        16 CompTIA Security+ and 19 CEH preparatory lab exercises based on these certifications’ performance-based exam objectives, which students can access remotely from anywhere, anytime, to develop knowledge and skills

·        Instructor syllabi to help integrate NCL labs and games into security classes

·        Games conducted 100% using cloud­‐based services, accessible from anywhere

·        Opportunities to follow the games as spectators

·        3 NCL Conferences (Eastern, Midwestern, and Western)

·        3 brackets to engage novice (Bronze), intermediate (Silver) and experienced players (Gold bracket)

·        Pre-season assessment to identify players with similar skill levels; players will be placed in one of three brackets based on skill level (Bronze, Silver, Gold)

·        Regular Season with 2 games optimized for individuals

·        Post-Season with two 5-10 player team-based games: NCL Conference and National championships

·        “Player Cards” and player/team statistics

·        Scenario-based, real-world games appealing to broad audiences (including men, women and non-dominant populations) to encourage engagement and passion

·        A strict Honor Code

Individual Award Certificateswill be presented for Regular Season game play to recognize players who are Top 10 in their conference and national brackets.

Team Award Certificates will be presented to Top 10 teams in their conference and national brackets.   

Students:

·       All Players who complete the regular season games and associated evaluations will receive Certificates of Participationto add to their professional portfolios and resumes.

·       To advance event sustainability, there will be a registration fee of $20 per playerto participate in the regular season and $25 per team for post-season play (via PayPal).

·       Registration opens August 17th, 2013 and closes September 30, 2013 at events.constantcontact.com/register/event?llr=pvd9yudab&oeidk=a07e7yev4b40d6f89d4. (There is also a link to the registration page from the NCL website.

·       Remotely accessible labs for CompTIA Security+ and EC Counsel Certified Ethical Hacker will be available August 24 through December 14, 2013.

·       Go to www.nationalcyberleague.org/fall13.shtml for additional information

·       You will need a faculty coach/mentor to register.

Faculty/Coaches:

·       To make it easier for you to integrate NCL activities into your classes, please see instructor syllabi for:

o   CompTIA Security+
o   EC-Council Certified Ethical Hacker (CEH)

·       Students participating in the 2013 NCL Fall regular season get access to hands-on labs to develop Security+ and CEH skills, 24x7, during the event period.

·       Students are required to have a faculty mentor/coach.  To serve as a faculty mentor/coach you will need to provide your students with your contact information, which they will submit in the registration process.  You will receive regular communications from the NCL, keeping you abreast of the latest developments.  Students should be able to contact you for counsel about these lab exercises. You will have opportunities to observe the NCL games in a virtual environment.  In reality, there is little actually required of you.

·       NCL participation is a great way to create enthusiasm and passion for cybersecurity education, to create student and school pride, and to develop and demonstrate knowledge and skills. It adds value to your classes, and it often improves student outcomes.

·       Please share this opportunity with your peers and students!

This is going to be really fun!

Thank you,

Dan Manson
NCL Commissioner

To join the NCL email list, please provide your name, email address, and college affiliation via email to info@nationalcyberleague.org.
Read More
Posted in ICT Education, James Jones, Security, Security; Identity Management, Teaching and Learning | No comments

Friday, 9 August 2013

Infographic: The Greatest Security Breaches In Internet History

Posted on 10:13 by Unknown

Infographic of the Day  fastcodesign

Hundreds of millions of people have lost their data to hackers, and it’s all big business’s fault.
Living Social gets hacked, and 50 million people have their name, address, and date of birth stolen. Credit-card information is safe, we’re assured, but it’s of little comfort. Plastic can be replaced. Identity? Not so much.

Yet Living Social is but one of many mega data breaches suffered in the Internet age, a point driven home by World’s Biggest Data Breaches, the latest infographic from David McCandless / Information Is Beautiful. The graphic visualizes all of those vaguely disconcerting security headlines from the past nine years into a tangible timeline of bubbles. So you can quickly spot the biggest breaches--like when Sony lost 77,000,000 user accounts over PSN, or when payment processor Heartland lost 130,000,000 accounts (which subsequently cost them about $140,000,000 in fines and settlements).
Aside from its sheer interest quotient, McCandless and co. added several small touches to keep the information interactive. Hovering over each bubble enlarges it for easy reading, and a click exposes a short story behind the unsettling figures. It’s just a pile of circles, but it’s tactile and explorable, tempting you to dig beneath the surface.

As for what one might learn from the graphic, I cannot say. Video game companies are the worst offenders, while banks seem to have staved off hackers (relatively) respectably. But is anyone going to change their lifestyle--give up Call of Duty or shove money in the mattress because their data may be stolen along with the faceless masses? Of course not.
Security breaches have become the power outage of the information age. They’re inevitable, devastating, and totally worth it for the convenience and pleasure we derive from the services that come under attack. Which is why, if you scroll below, you’ll find my social security number, blood type, mother’s maiden name, and everywhere I’ve ever lived. I’ve also enclosed a few semiclad selfies in case you haven’t checked my Instagram lately.
See more here.
[Hat tip: Mashable]

Mark Wilson

Mark Wilson is a writer who started Philanthroper.com, a simple way to give back every day. His work has also appeared at Gizmodo, Kotaku, PopMech, PopSci
Read More
Posted in James Jones, Security, Security; Identity Management | No comments

Friday, 2 August 2013

Identity Week: Burlingame, CA; Nov 11-15

Posted on 10:13 by Unknown


TechEDge eNews Update | 2 August 2013 | http://ccctechedge.org

Leading Technology In Education For California's Future

Identity Week: Burlingame, CA; Nov 11-15


Registration is now open for Identity Week, November 11-15, 2013, held in Burlingame, California, just south of San Francisco. California Community Colleges IT staff are encouraged to attend.

The event, led by Internet2, will bring together the InCommon community, identity management technical implementers and architects, and U.S. and international leaders in the field of identity and access management.

Each meeting has a separate registration, so you can choose the one(s) right for you. For links to each of these meetings, the online registration process, and the hotel registration site, please visit www.incommon.org/idweek.

CAMP Pre-Conference Workshop: Getting Started with Federated Identity Management (Nov. 13) - Those just getting started with identity management will be interested in this Wednesday afternoon workshop. The program will focus on the primary principles that underlie an effective identity management system, look at how federated IdM fits and why it is important, and introduce you to InCommon. There is a separate registration for the pre-conference. More information is at: https://spaces.internet2.edu/display/CAMP2013/Getting+Started+with+Federated+Identity+Management

CAMP: Managing Identity and Access in an Era of Distributed Services (Nov. 14-15): CAMP will focus on the policy and technical challenges of implementing outsourced and cloud services. CAMP includes two tracks, “Ramping Up for Distributed Services,” and “Federation and Distributed Services: What’s Working and What’s Next.” The program for both tracks is posted on the CAMP website, https://spaces.internet2.edu/display/CAMP2013

The week kicks off on Monday, November 11, with a meeting of REFEDS, the international organization for operators and architects of identity federations. You can find out more about REFEDS at https://refeds.org/about_agreement.html.

If you have questions about Identity Week or registration, please see the FAQ on the website or contact Dean Woodbeck at woodbeck@internet2.edu.

-----
Dean Woodbeck
Program Manager, InCommon
Internet2
Read More
Posted in Educational Technology, ICT Infrastructure, James Jones, Networking, networking security, Security, Security; Identity Management | No comments
Older Posts Home
Subscribe to: Posts (Atom)

Popular Posts

  • NPD: US homes now hold over 500m Internet-connected devices with apps, at an average of 5.7 per household
    The Next Web Emil Protalinski Contact Author 18 March 2013               There are now more than 500 million devices in US homes...
  • The Myth of Population Density and the High Cost of Broadband
       Feb 01, 2013 12:55 PM PST, CircleID By Bill St. Arnaud One of the enduring myths that is used by apologists for incumbent...
  • CompTIA: Why Are We Still Talking About Security?
    by Seth Robinson on Thursday, November 14, 2013   CompTIA Security may not be as hyped as other tech trends like cloud computing, mobility o...
  • California Community College Funding Still Low
    March 26, 2013 Dear California CC, The Public Policy Institute of California released a report this morning that documents the budget imp...
  • WebProfessionals.org Announces STEM to STEAMIE Initiative
    By adding three key elements, WebProfessionals.org aims to expand and convert the fields of study representing Science, Technology, Engineer...
  • Free Winter ICT Educator Conference Presentations
    The Winter 2013 ICT Educator Conference is January 3-4, 2013 in San Francisco. You can join most presentation sessions for free, from any br...
  • CompTIA A+ Certification Marks 20th Anniversary
    Mar 21, 2013, CompTIA Worldwide vendor-neutral certification still on cutting edge of technology Downers Grove, Ill., March 21, 2013 – In a...
  • CA Career Briefs - Preparing for Change
    October 30, 2012 Prepare for Change ...
  • Code.org Launches To Help Make Computer Programming Accessible To Everyone
    Drew Olanoff ,  TechCrunch       Drew Olanoff has over 10 years of marketing, PR, customer service and support, relationship buildin...
  • IT budgets, headcount set to grow in 2014: study
    Companies are increasing IT spending, yet economic uncertainty remains a concern, SIM reports. By Ann Bednarz , Network World November 12,...

Categories

  • Big Data
  • CATV
  • CENIC
  • Certifications
  • Cloud
  • Computational Thinking
  • Computer Engineering
  • Computer Science
  • CTE
  • Database
  • Digital Divide
  • Digital Literacy
  • Digital Media
  • Diversity
  • Educational Technology
  • elearning
  • Electronics
  • Entrepreneur
  • ethics
  • funding opportunity
  • Gaming
  • GIS
  • Grants
  • Hacking
  • Healthcare IT
  • ICT Applications
  • ICT Core Competencies
  • ICT Education
  • ICT Infrastructure
  • ICT Jobs
  • ICT pathways
  • ICT Regulation
  • ICT Research
  • Industry News
  • Innovation
  • Internships
  • James Jones
  • K-12
  • law
  • Linux
  • Mobility
  • MOOC
  • MPICT Announcements
  • Multimedia
  • Networking
  • networking security
  • Olivia Herriford
  • Open Source
  • Operating Systems
  • Pierre Thiry
  • Piracy
  • Public Policy
  • Security
  • Security; Identity Management
  • Smart Grid
  • Social Media
  • Soft Skills
  • Software Assurance
  • Software Engineering
  • Spanish
  • STEM Education
  • Storage
  • Teaching and Learning
  • Telecom
  • Tools
  • virtualization
  • Web
  • WIB
  • Wireless
  • women
  • Women in ICT
  • Workforce Development

Blog Archive

  • ▼  2013 (418)
    • ▼  November (41)
      • NSA 'infected' 50,000 networks with malware
      • Techies must nip growing scorn in bud
      • Is the tide turning? Women filled 60% of tech jobs...
      • Transfer Program Between California Community Coll...
      • Talent Shortage May Impede New Hiring by Technolog...
      • Time for the United States to Re-Skill ?
      • Tim Berners-Lee says 'surveillance threatens web'
      • Start a Microsoft TEALS Computer Science Program f...
      • 7 Ways to Find the Best IT Jobs
      • Cal Poly Announces Major New Initiative In Cyberse...
      • WebProfessionals.org Announces STEM to STEAMIE Ini...
      • US Department of Labor: $100m Youth Career Connec...
      • CompTIA: Why Are We Still Talking About Security?
      • New Milestone for CompTIA Troops to Tech Careers I...
      • HP: 90% of Apple iOS mobile apps show security vul...
      • Career tech at community colleges should not be un...
      • ITIF: A Guide to the Internet of Things
      • Guardian: Cyber-attacks eclipsing terrorism as gr...
      • CTI: Tech Leaders Warn IT Talent Shortage Could C...
      • Robert Half Technology 2014 Technology Salary Guid...
      • 5 Technology Jobs That Didn’t Exist 5 Years Ago
      • ATE@20: MPICT Runs Three Tests of International T...
      • Please Sign Petition to Make Computer Science Coun...
      • Opinion: The Case for Citywide Broadband in LA
      • New broadband report reveals £20 return on every £...
      • IASE Unclassified Cyber Awareness Challenge
      • LearningWorks: THE MISSING PIECE: Quantifying Non...
      • IT budgets, headcount set to grow in 2014: study
      • IBM to Announce More Powerful Watson via the Internet
      • Here Come the WiFi Drones
      • Netflix, YouTube Account for 50% of North American...
      • Quick Tips: Flip Your Class
      • New CompTIA Mobility+ Certification Addresses Skil...
      • Bay Area Computer User & Network Support Marketpla...
      • Los Angeles Citywide Gigabit Fiber RFP: Is This th...
      • Microsoft and Facebook offer bounties to bug hunters
      • How Much Media? 2013
      • Hour of Code Tutorials Are Ready to Try - 1.5m Stu...
      • ICT jobs in California ripe for the picking
      • Joint Workforce Development, CBO and MPICT Webinar...
      • Center for Community College Student Engagement Re...
    • ►  October (53)
    • ►  September (44)
    • ►  August (21)
    • ►  July (30)
    • ►  June (28)
    • ►  May (43)
    • ►  April (43)
    • ►  March (35)
    • ►  February (43)
    • ►  January (37)
  • ►  2012 (82)
    • ►  December (25)
    • ►  November (40)
    • ►  October (17)
Powered by Blogger.

About Me

Unknown
View my complete profile